One-click Approve & escalate on the approval card: answers the pending request and switches the live session to a permission preset.
Install
# from GitHub (first run asks for allowBuilds approval — follow the hint, retry)
dsh plugin --profile web add github:almazom/dsh-almazom-approve-escalate
Any plugin you install runs third-party code with your own permissions — it can read your files, use your credentials, and reach the network, and tool approvals don’t sandbox it. GitHub-sourced plugins also run build scripts at install time — pnpm blocks those until you allow them, so an install can stop with ERR_PNPM_GIT_DEP_PREPARE_NOT_ALLOWED or ERR_PNPM_IGNORED_BUILDS; dsh prints the exact key to add under allowBuilds in your profile’s pnpm-workspace.yaml, and the install works on the next run. Allowing a build is a trust decision: only install sources you trust, and pin a commit (github:owner/repo#sha).
README
One click on the DSH web approval card: approve the pending request and switch the live session to full access (danger-full-access: sandbox off, no further approval prompts) — plus a /yolo composer command that switches the permission preset without a pending request.
Isolated third-party plugin. No harness core changes, no telemetry, no secrets.
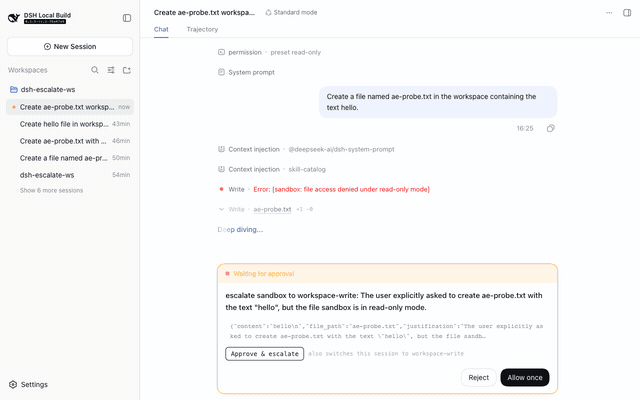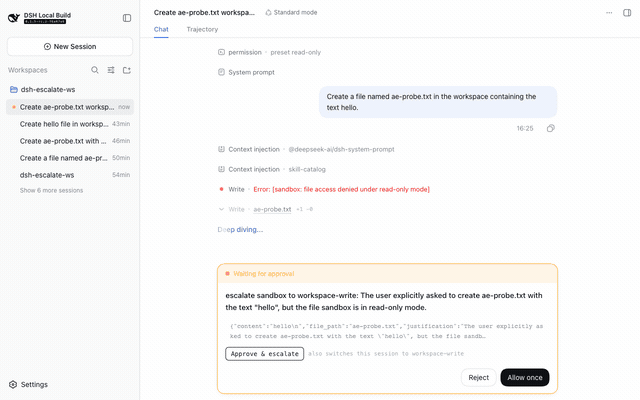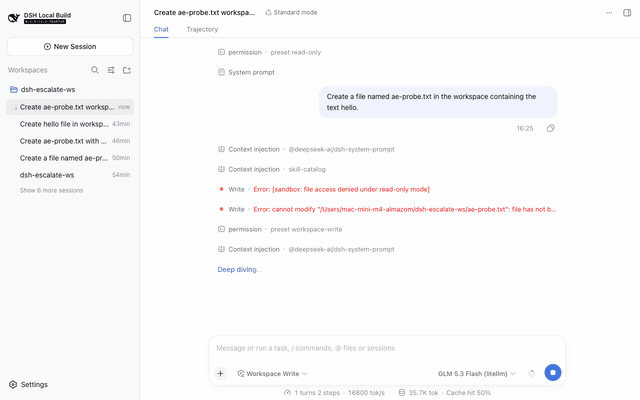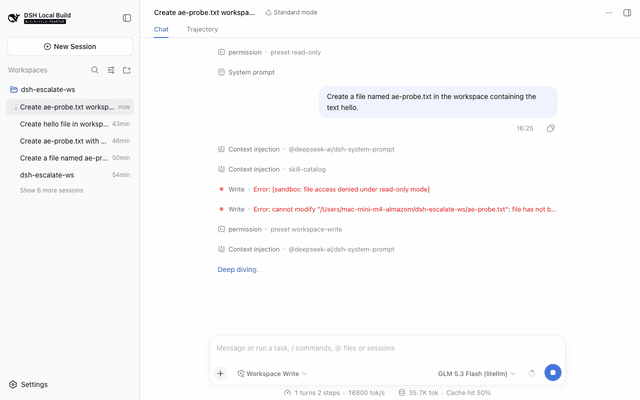
What you get
The approval card ("Waiting for approval") grows one extra action above the shipped Reject / Allow once row:
- Approve & full access — dispatches
/permission danger-full-accesson the live session (the same command the shipped/permissionpicker uses) and then answers the pending request as Allow once. A warning line spells out that future approval prompts are disabled. - /yolo — composer command (slash menu) that switches the session to full access without a pending request; the status chip flips to Full access.
- Both shipped buttons keep working; the plugin only composes two manual actions into one click. If the host lacks the
/permissioncommand, the button says so instead of answering blind.
Install
dsh plugin --profile web add dsh-almazom-approve-escalate
(or from git: dsh plugin --profile web add git+https://github.com/almazom/dsh-almazom-approve-escalate.git)
After installing, hard-refresh the browser so the client bundle picks up the new rev.
Then restart the web app (dsh web / your service manager) and hard-refresh the browser.
Configure
Override the preset or the label in the profile patch layer (~/.dsh/profiles/web/cordis.patch.yml or $DSH_HOME/cordis.patch.yml):
- insert:
    - id: almazom-approve-escalate
      name: 'dsh-almazom-approve-escalate'
      config:
        preset: 'workspace-write'   # any permission preset your host offers
        label: 'Approve & escalate'
Updates & versioning
- The plugin is versioned in
package.json(semver) and deployed as git commits in this repo; the profile mounts it vialink:so new code is served live at a fresh client-bundle rev. - Reload rule: already-open app pages keep the module graph they booted with. After any deploy, hard-refresh the DSH tab (PWA on iPhone: close from multitask, reopen). The deploying agent must announce every client-affecting change via Delta Chat ("обнови вкладки DSH").
- Rollback:
dsh plugin --profile web remove dsh-almazom-approve-escalateor delete the patch row — features disappear without touching the host.
Rollback
dsh plugin --profile web remove dsh-almazom-approve-escalate
(or delete the insert row above). No host files besides the profile's own node_modules and patch layers are touched.
Security & trust
- Plugins hold full host privileges — review the source before installing. It is two hand-written files:
lib/index.js(host: serves the config JSON above) andlib/client.js(browser: the button). - The client bundle uses the official plugin surfaces only: the documented
conversation.approval.detailslot, theslots/sessionsclient services, and the live-session command API. It never touches the network beyond same-origin config/config fetches; there is no outbound traffic. - The escalation reuses the operator-auditable
/permissioncommand path — the switch is logged like a manual one.
Compatibility
Built and verified against DeepSeek Harness 0.1.5-rc.x. The client contract it relies on (loader wrapper, slot key, seats) is documented for third-party plugins; a shipped-bundle refactor of the approval card may require a plugin update.
Provenance
- Developed against upstream
deepseek-ai/deepseek-harnessatc291e79; live-verified on a0.1.5-rc.2host with a real approval flow (seedocs/for the recording). - No model round is involved in the plugin itself; the verification recording used one model round to trigger a genuine approval request.
- Related: discussion #6616 (the /permission picker fix this plugin's escalation path builds on).
License
MIT
Links
More in this category
kenryu42/cc-safety-net★ 1900
Pre-execution guard that blocks destructive Git and filesystem commands and access to secrets such as SSH keys and .env files before a tool call runs.
ADWMC/helm-d#helmd★ 984
Security-analysis plugin for DeepSeek Harness: 33 tools spanning six security domains, evidence/reporting and toolbox, plus the case lifecycle, routing and tool ledger; a session-bound case workflow with an evidence chain, E-id validation and reproducible findings; 362 on-demand references; three hot-swappable persona profiles; and a four-tab workbench (armor / case / intercept / about) with case-state recovery after context compaction.
toby-bridges/api-relay-audit★ 904
Runs local security audits of AI API relays and LLM proxies from DeepSeek Harness, producing Markdown reports for prompt injection, model substitution signals, tool-call rewriting, error leakage, stream integrity, and profile-gated Web3 risks.
SeaOf0/dsh-redteam-model★ 807
Authorized-security DSH collection: nine work modes (redteam coordinator, pentest, code audit, binary analysis, attack-defense, AV evasion, incident response, cloud security, CTF solving) and fifteen runtime plugins, managed from a settings page with one-click deploy, install, update and uninstall.
howmp/dsh-pentest★ 616
Authorized pentest mode for DeepSeek Harness — exploration chain, assets and findings with a Web view.
PerryLink/dsh-auto-review★ 244
Second-model auto-review on the approval answerer chain: a read-only reviewer subagent returns structured allow/deny verdicts with reasons, fail-closed by default.
Community comments
Comments are public GitHub Discussions. Loading them connects to GitHub and Giscus; a GitHub account is required to post.