Writes local JSONL summaries of per-turn tool counts and coarse verification signals without storing prompts, tool arguments, or result text.
Install
# from npm (prebuilt)
dsh plugin --profile web add dsh-verification-receipt
# from GitHub (first run asks for allowBuilds approval — follow the hint, retry)
dsh plugin --profile web add github:030611/dsh-verification-receipt
Any plugin you install runs third-party code with your own permissions — it can read your files, use your credentials, and reach the network, and tool approvals don’t sandbox it. GitHub-sourced plugins also run build scripts at install time — pnpm blocks those until you allow them, so an install can stop with ERR_PNPM_GIT_DEP_PREPARE_NOT_ALLOWED or ERR_PNPM_IGNORED_BUILDS; dsh prints the exact key to add under allowBuilds in your profile’s pnpm-workspace.yaml, and the install works on the next run. Allowing a build is a trust decision: only install sources you trust, and pin a commit (github:owner/repo#sha).
README

Ask a smaller, checkable question: what verification-shaped execution signals did DSH record this turn?
dsh plugin --profile web add dsh-verification-receipt
The receipt summarizes recorded tool counts and lexical verification-shaped signals. It does not prove that tests ran or that code is correct.
Community-maintained and not an official DeepSeek project. Related trust-layer plugins: Telemetry Redactor, Evidence Audit, and Context Provenance.
DSH Verification Receipt is a small, passive Profile Bundle for DeepSeek Harness. After each durable turn/end, it appends one privacy-minimal, heuristic execution summary to a local JSONL file.

It records execution traces, not semantic correctness. A receipt shows only that DSH logged tool calls and that a lexical heuristic found a possible verification signal. It never proves that a test ran. It cannot show that the right command executed, that assertions were sufficient, that output was truthful, or that the assistant's conclusion was correct.
This is intentionally not an evidence-audit ledger: rows stay independent and there is no hash chain, artifact capture, claim-evidence linkage, or protocol attestation.
Compatibility evidence
Version 0.1.1 supports exactly DSH 0.1.2-alpha.3, 0.1.2-alpha.4, and 0.1.2-alpha.5 on Node.js ^22.19.0 || >=24.0.0. Each release passed local package gates and disposable Windows Web Profile install, composed-config, cold-start, and uninstall acceptance. See the compatibility evidence for the exact boundary. Cordis and Session are optional host peers because DSH supplies their runtime services; Schemastery is included as an exact runtime dependency and also declared as a compatibility peer.
Install
Add the published package to every profile that should emit receipts:
dsh plugin --profile web add dsh-verification-receipt
dsh --profile web --dump-config
Repeat the first command with another profile name (for example, headless) when that profile also needs receipts. For local development, clone this repository, run pnpm install --frozen-lockfile && pnpm run check, and pass the checkout path to dsh plugin ... add instead of the package name.
package.json declares dsh.bundle.patch; cordis.patch.yml inserts one ordinary observer plugin. It works on any DSH surface that provides the core Session service.
Output
The image below shows a real receipt emitted by the released plugin code over synthetic, non-user DSH events; the right side displays selected persisted fields only. It is not a user conversation and does not prove that tests ran or passed.
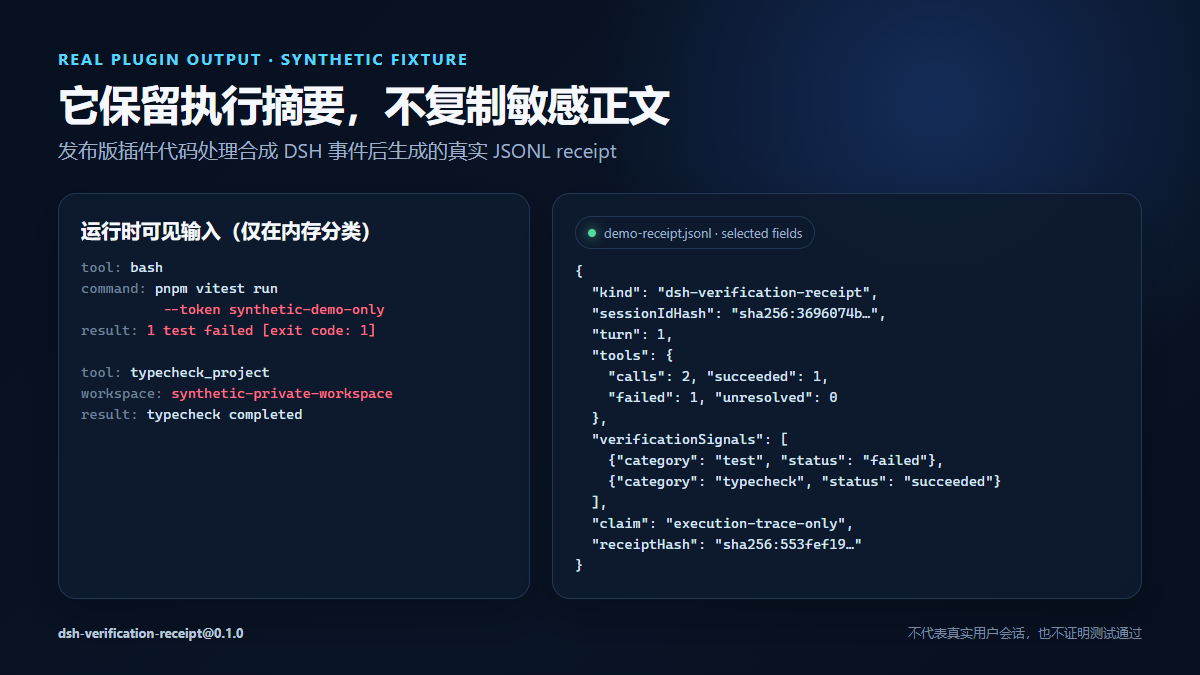
The default file is:
$DSH_HOME/verification-receipts/v1/receipts.jsonl
When DSH_HOME is unset, it resolves below ~/.dsh. Override it with an absolute path in the profile's cordis.patch.yml:
- id: verification-receipt
  config:
    outputPath: /absolute/private/path/receipts.jsonl
Each line has this form:
{
  "schemaVersion": 1,
  "kind": "dsh-verification-receipt",
  "sessionIdHash": "sha256:…",
  "turn": 3,
  "turnEndSeq": 42,
  "endedAt": 1786630000000,
  "outcome": "completed",
  "tools": {
    "calls": 4,
    "succeeded": 3,
    "failed": 1,
    "unresolved": 0,
    "topLevel": 2,
    "nested": 2
  },
  "verificationSignals": [
    {
      "source": "command",
      "category": "test",
      "status": "failed"
    }
  ],
  "claim": "execution-trace-only",
  "receiptHash": "sha256:…"
}
Integrity warning
Both hashes are unkeyed and recomputable. receiptHash is SHA-256 over the exact preceding receipt fields in their emitted order. Anyone who can edit a row can recompute it. Independent rows do not reveal deletion, insertion, reordering, truncation, rollback, or replacement. The hash is neither a signature nor a trusted timestamp, hash chain, commitment, or tamper-evident log.
Privacy and agent behavior
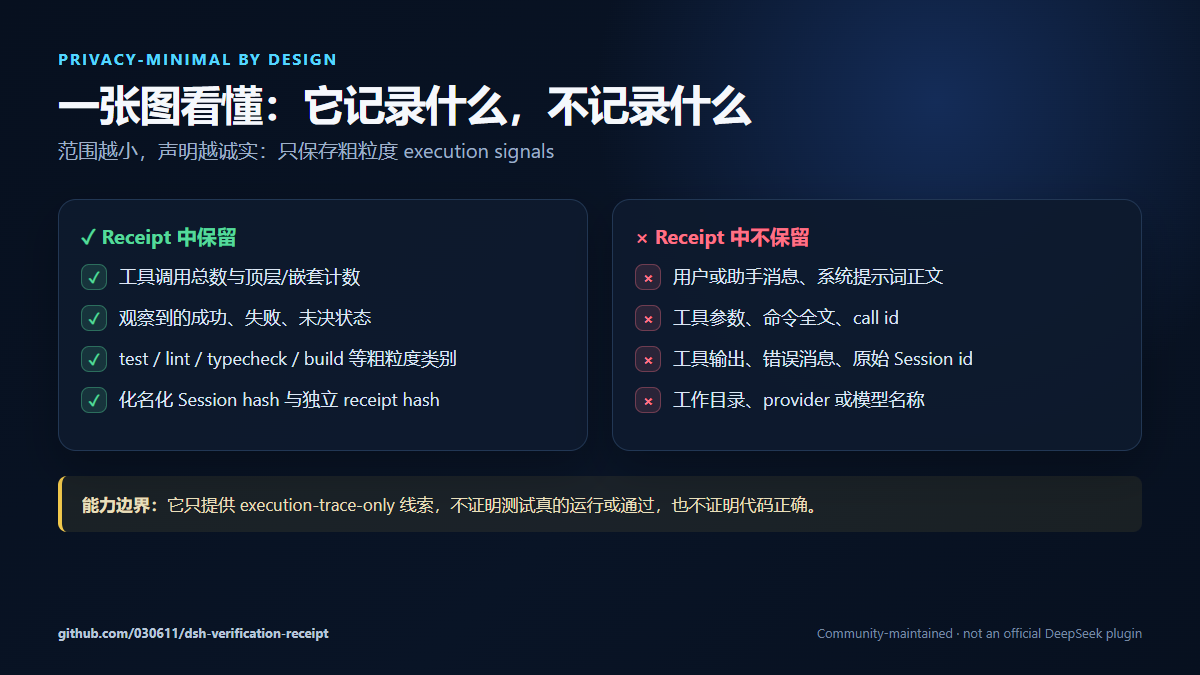
The persisted receipt does not contain:
- tool arguments or call ids;
- tool result content or error messages;
- assistant or user message text;
- raw session ids, working directories, provider names, or model names.
The plugin temporarily reads tool names, raw arguments, and result status from existing durable events to compute the summary. It does not persist those inputs, append a Session event, register a tool, add a prompt section, inject context, make a model call, or change model history.
sessionIdHash is deterministic, unkeyed, and domain-separated so receipts from one Session can be grouped without storing its raw id. It is linkable across files. If a Session id is predictable or low entropy, an observer can guess candidates offline and recompute the hash; this is pseudonymization, not anonymization.
Verification-signal heuristic
A heuristic signal is emitted when either:
- a tool name resembles test, typecheck, lint, build, check, verify, or validate work; or
- a shell-like tool's in-memory
commandorcmdargument resembles such work.
The stored signal keeps only source, coarse category, and observed status. Native DSH tool errors and recognized non-zero shell exit markers count as failure. Background commands remain unresolved because their later job result may occur outside this turn. Even status: succeeded means only that the observed call completed without a recognized failure marker; it does not mean tests passed or even ran.
Classification is lexical; it does not parse shell syntax, expand aliases, or execute commands:
| Input shape | Support | Boundary |
|---|---|---|
JSON-string or object arguments with string command/cmd |
Supported | Only recognized shell-like tool names are inspected. |
Upper/lower case, quotes, or visible wrappers such as bash -lc/pwsh -Command |
Supported lexically | A category keyword must remain visible in the string. |
Array commands, argv, nested command objects, custom shell tool names |
Unsupported | No signal is emitted. |
| Aliases or wrappers with no visible category keyword | Unsupported | False negatives are expected. |
Quoted prose such as echo "do not run tests" |
Lexically matched | False positives are expected because intent and execution are not parsed. |
Treat every match as a discovery hint named “heuristic signal,” never as “tests ran,” an attestation, or a quality gate.
Model experience
| Aspect | Effect |
|---|---|
| Token cost | None. |
| Tool calls | None; the model gets no new tool. |
| Session log | Unchanged; the plugin reads existing events and adds no events. |
| Prompt and context | Unchanged. |
| Turn latency | The listener scans the completed turn synchronously and queues local file I/O; it does not await disk on the turn path. |
Known limitations
- Receipts cover events observed by the running plugin. Constructor seed history and turns completed while it was unloaded are not backfilled.
- A process crash can lose a queued receipt because
turn/enddoes not synchronously wait for this optional local sink. Normal plugin/application disposal drains accepted writes. - Disposal first closes the enqueue gate, then unregisters listeners, then drains accepted writes. Abrupt process termination cannot run that lifecycle.
- Receipt rows are independent; deletion, reordering, truncation, and rollback are not detectable.
- Receipt status repeats DSH's recorded tool outcome and recognized shell markers. It does not independently execute or validate anything.
- Projection cost grows with the number and size of events in a turn; unusually large tool arguments can add end-of-turn CPU time while they are classified in memory.
- The in-process write queue is ordered but unbounded. A slow or stuck filesystem can grow memory usage until writes recover or the process ends.
- There is no cross-process lock. Two DSH processes targeting one file have no guaranteed row order or row-boundary integrity; use one file per process. A crash can leave an incomplete final line, which readers must reject or quarantine.
- Creation modes request
0700/0600on supporting POSIX filesystems only. Existing permissions are not tightened, Windows may ignore POSIX modes, and pre-existing symbolic links are followed. Configure a trusted, private, non-symlink path. - The file has no built-in rotation, retention, encryption, signing, or recovery.
See SECURITY.md for the trust and disclosure model.
Development
pnpm run typecheck
pnpm run test
pnpm run build
pnpm run check
pnpm run release:smoke
pnpm run performance:smoke
Tests cover privacy exclusions, deterministic hashing, top-level and Code Mode final states, the supported/unsupported classification matrix, listener disposal, disk draining, and a real DSH Context + SessionStore composition. release:smoke enforces the exact tarball file list, installs the real .tgz into a temporary project, and imports it by package name.
License
MIT
Links
More in this category
toby-bridges/api-relay-audit★ 860
Runs local security audits of AI API relays and LLM proxies from DeepSeek Harness, producing Markdown reports for prompt injection, model substitution signals, tool-call rewriting, error leakage, stream integrity, and profile-gated Web3 risks.
SeaOf0/dsh-redteam-model★ 638
Authorized-security DSH collection: nine work modes (redteam coordinator, pentest, code audit, binary analysis, attack-defense, AV evasion, incident response, cloud security, CTF solving) and fifteen runtime plugins, managed from a settings page with one-click deploy, install, update and uninstall.
howmp/dsh-pentest★ 558
Authorized pentest mode for DeepSeek Harness — exploration chain, assets and findings with a Web view.
PerryLink/dsh-auto-review★ 206
Second-model auto-review on the approval answerer chain: a read-only reviewer subagent returns structured allow/deny verdicts with reasons, fail-closed by default.
NanmiCoder/dsh-auto-mode★ 163
Adds an Auto permission preset between Workspace Write and Full access: routine work stays in the official workspace-write sandbox while the current session model reviews escalation and destructive calls, granting one exact wider access once, asking when the intent is ambiguous, and denying critical paths.
PerryLink/dsh-permission-rules★ 114
Claude Code-style declarative permission rules: ordered allow/deny/ask YAML rules matching tool names, arguments, workspace paths, and agent identity on the tools/pre-execute waterfall, with full session-log audit, dry-run mode, and hot reload.
Community comments
Comments are public GitHub Discussions. Loading them connects to GitHub and Giscus; a GitHub account is required to post.